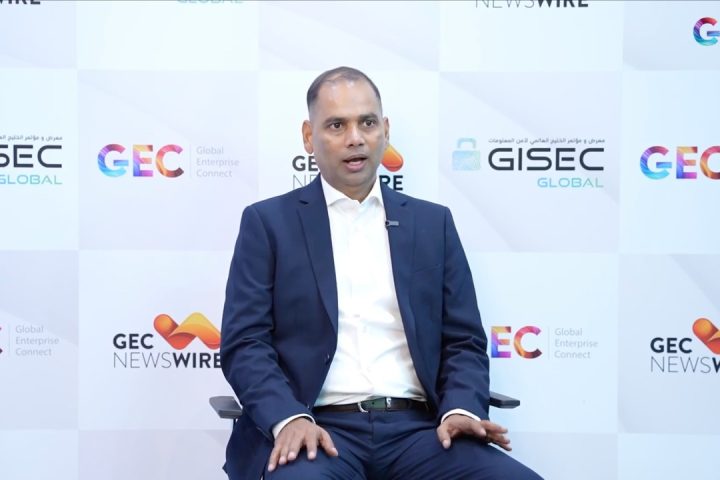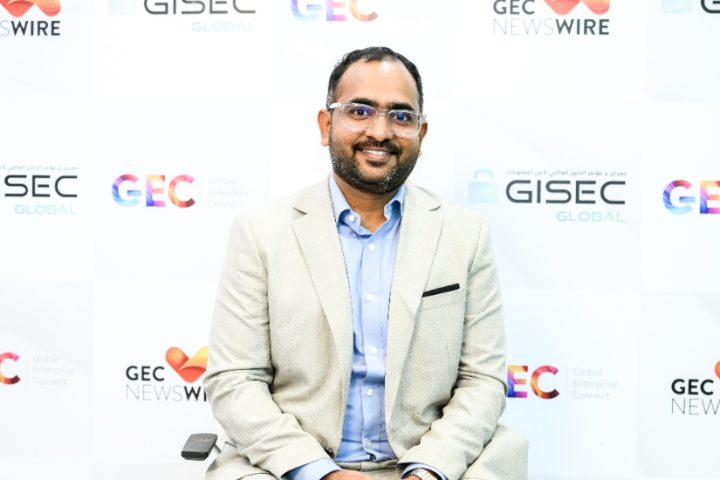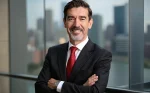


Ram Narayanan, Country Manager, Check Point Software Technologies, Middle East, told GEC Newswire that the gap between AI adoption and AI security is now the defining exposure, and that detection alone cannot close it.
The most quoted number at GISEC came from Check Point’s own research. Ram Narayanan, Country Manager, Check Point Software Technologies, Middle East, said 70% of enterprises have started adopting gen AI applications while only 26% have security controls around them. Neither the report nor its sample was specified in the interview.
What has changed underneath that gap is how enterprises see their own estate. Security used to be examined one layer at a time. “People were looking at it in silos. What about network? What is on the endpoint? What is about cloud adoption?” Narayanan said. Connected infrastructure with AI running across it produces a different picture, and businesses now assess risk the same way.
Consolidation has stopped meaning fewer products
Vendors have pitched consolidation for years, Check Point among them, and the old version counted licences. An enterprise running 30 or 40 technologies was told to run fewer. Narayanan said the argument has moved. Value now sits in a single policy management platform, one place to apply policy, and visibility across the organisation. “It’s not just reduction in the number of products,” he said.
The corollary is a shift away from waiting to be attacked. Attacks running at AI scale outpace identification and response, which puts the emphasis on stopping them at the point of exposure. Narayanan’s example is ordinary enough to be uncomfortable: an employee uploading confidential material to a public AI tool for analysis. Once it leaves the network it is gone, so the control belongs at the endpoint, where the user meets the application, and it should tell the employee what policy they just breached.
Thousands of alerts, and no way to say which 10 matter
Narayanan said the problem is not the technology. Risk has scaled because employees reach for publicly available AI tools alongside whatever the business has sanctioned, which leaves visibility over what staff are actually using as the first requirement. On agents, he described controls over what they are permitted to do as they reach data and applications, with guardrails defining the boundary.
The harder problem is triage. Regional enterprises have invested heavily and generate thousands of alerts, with frontier models accelerating vulnerability exploitation. “Out of those thousands of alerts, which needs to be prioritized, because not all of them are equal,” he said. Exposure management, with business context attached to each risk, is where he expects customers in the region to go next.