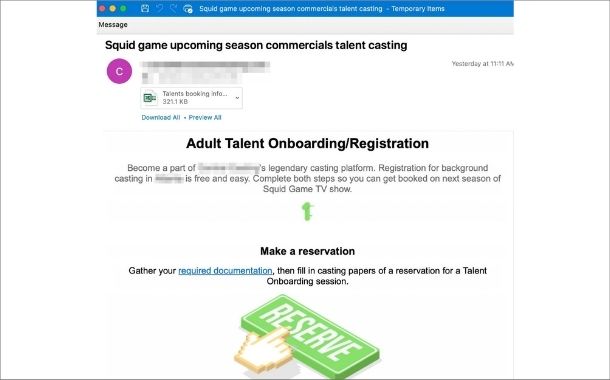
Proofpoint identified the large cybercrime actor TA575 distributing Dridex malware using Squid Game lures. The threat actor is purporting to be entities associated with the Netflix global phenomenon using emails enticing targets to get early access to a new season of Squid Game or to become a part of the TV show casting.
On October 27, 2021, Proofpoint observed thousands of emails targeting all industries primarily in the United States. The emails used subjects such as:
- Squid Game is back, watch new season before anyone else.
- Invite for Customer to access the new sesason. [sic]
- Squid game new season commercials casting preview
- Squid game scheduled season commercials talent cast schedule
The emails tell the victim to fill out either an attached document to get early access to the new season of the show or a talent form to become part of the background casting. The attachments are Excel documents with macros that, if enabled, will download the Dridex banking trojan affiliate id “22203” from Discord URLs. Dridex is a prolific banking trojan distributed by multiple affiliates that can lead to data theft and installation of follow-on malware such as ransomware.
“Threat actors worldwide are continuing to target people with agile and relevant attacks. At Proofpoint we see 94% of cyberattacks starting via email, and more than 99% of those requiring human interaction to activate and enable the attack,” said Emile Abou Saleh, Regional Director, Middle East and Africa for Proofpoint.
“In addition, Proofpoint’s recent regional research found that 70 % of CISOs/CSOs in the UAE believe that human error was one of the biggest risk factors for their organization. As these threats grow in scope and sophistication, it is critical that organizations and people alike shore up their defenses against email fraud by adopting cybersecurity software to protect themselves from threat actors. Companies need to remain alert and foster a strong security culture through effective and ongoing security awareness training. ” he concluded.
TA575 is a Dridex affiliate tracked by Proofpoint since late 2020. This group distributes malware via malicious URLs, Microsoft Office attachments, and password-protected files. On average, TA575 sends thousands of emails per campaign impacting hundreds of organizations. TA575 also uses the Discord content delivery network (CDN) to host and distribute Dridex. Discord, a communications platform with consumer and enterprise uses, is an increasingly popular malware hosting service for cybercriminals.
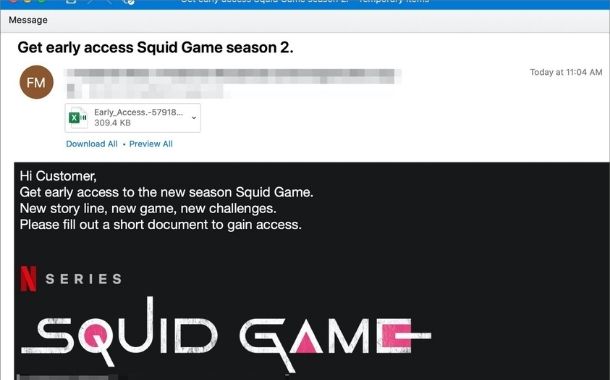
TA575 themes generally include invoicing and payments, but occasionally include popular news, events, and cultural references. Cybercriminal threat actors in general have pounced on Squid Game as a popular lure and malware theme. This makes sense; as Squid Game is Netflix’s “biggest ever” series, the pool of potential victims who would inadvertently interact with malicious content associated with it is higher than a general lure theme. TA575 is betting the invitation to be part of the upcoming season will entice more users to interact with the malicious Microsoft Excel file.