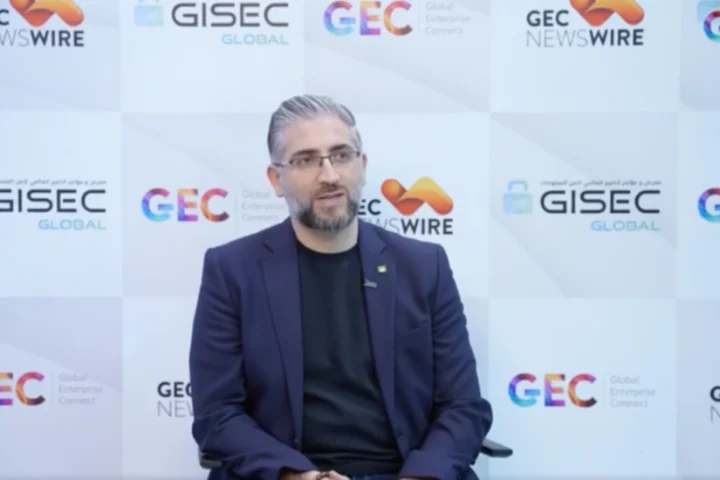


Adnan Bassem Fakhouri, Customer Delivery and Success Engineer at QuantumGate, on why budgets and roadmaps for post-quantum cryptography have raced ahead of the one task that has to come first.
Two thirds of UAE entities have set aside money to move off classical encryption. Just over a third can say what encryption they are currently running.
That gap is the most useful thing in QuantumGate’s latest regional readiness findings, presented at GISEC Global in Dubai, and Adnan Bassem Fakhouri, Customer Delivery and Success Engineer at QuantumGate, reads it as a sign of progress rather than a warning. The reasoning behind that reading is worth following, because it changes what a security leader should do about it this quarter.
The figures come from a QuantumGate survey of entities in the UAE and wider MENA region. The company did not publish a sample size or methodology alongside the findings, and the data has not been independently verified, so the percentages are best treated as directional rather than as a measurement of the whole market.
Budget arrived before inventory, which is the wrong order and still good news
“64% of the entities have already budgeted for a transition to PQC,” Fakhouri said. For a migration that has no regulatory deadline attached to it in most sectors, and no single vendor to buy it from, a committed line in the budget represents a decision that someone senior has already made.
Fakhouri reads it as an admission about scale. “It means that a lot of these entities are already focused on creating a budget because they know that this transition will take time, money, and effort,” he said. Organisations do not budget years ahead for work they think they can absorb into business as usual.
Planning tracks the money closely. Roughly 42% of the entities surveyed are already building migration roadmaps, with a similar proportion at the point of starting one. “Whether you look at it from a budgetary standpoint or a roadmap standpoint, we see readiness in the region over there,” Fakhouri said.
A cryptographic inventory is a young discipline, not a neglected one
Then there is the 35%, the share of entities with a working picture of their own cryptographic material, and the number Fakhouri says the industry should be watching most closely.
Taken alone it looks like a readiness problem. He puts it in a different context. “The idea of creating a cryptographic inventory is novel. It’s been brought up many times in the context of PQC and not in other cybersecurity-related topics,” he said. Asset inventories, vulnerability inventories and software bills of materials are all established practice. Nobody was asking organisations to catalogue every certificate, key exchange and algorithm across their estate until quantum migration made it necessary.
The trajectory is what matters to him. “If you asked the same question five years ago, this would have been maybe less than 5%,” Fakhouri said. “So the fact that it’s at 35% already, it means that discovery has started. It means that the entities are thinking about the inventory.”
He is not treating it as sufficient. QuantumGate intends to track the figure across successive reports, and Fakhouri set the target where it has to sit for a migration of this kind to work. “We need this number up at 100%. We need to know all of the cryptography across all of the critical government sectors.”
Sensitivity of data, not calendar length, sets the start date
Asked what a security leader should do first, Fakhouri put discovery ahead of everything, including technology selection. “When I have a clear vision of what I have in my systems, of the criticality of those systems, I can then create a very well-defined plan,” he said.
His definition of that plan extends well beyond architecture. “The plan isn’t just the technology, the plan is the budget, the plan is the people, the plan is the regulation, the plan is the compliance,” he said.
Timelines interest him less than most vendors in this market would admit. One year, six months, three years, the duration is a consequence of the estate rather than a target to hit. What drives urgency is the data itself, and his formulation leaves little room to defer. “If your data is highly sensitive, you should have started last week. If your data is not sensitive, you should start today.”
The logic behind that is the harvest-now-decrypt-later exposure that makes post-quantum migration unlike other security upgrades. Encrypted traffic captured today can be stored until a machine capable of breaking it exists. Data with a long confidentiality requirement is already at risk, and no amount of future migration retrieves what has already been collected.
Migration runs on the supply chain, and customers have started applying pressure
The part of the transition that organisations most often underestimate is how little of it they control directly.
“Replacing cryptography won’t happen overnight, and it’s not going to be by, I replace one system and then the other system will follow,” Fakhouri said. “Many different vendors, even vendors that sell perhaps the same type of technology, need to be notified when an entity begins its transition.”
QuantumGate has used GISEC to work that problem from the vendor side, asking suppliers directly when PQC-ready products will be generally available and when they will be available to critical government entities. Those conversations have a prerequisite that sits with the customer, and it is the inventory again in a different guise. An entity needs to know what cryptography each vendor supplies and exactly where in the infrastructure each product sits.
With both facts established, procurement becomes leverage. Fakhouri described the conversation an entity can then have at renewal, telling a supplier that its product runs in a critical system, that the contract is up, and that the system needs to be PQC-capable because the migration has happened around it. “So now we see the entities and the customers putting some more soft pressure on the vendors to begin coming up with a plan to migrate their current technologies to PQC,” he said.
Peer visibility moves the market faster than mandates
The last factor Fakhouri raised is the one least amenable to a project plan, and in his account the most powerful.
Sectors move together or they stall together. An industry in which most participants migrate while a few hold out ends up carrying the risk of the holdouts, and the pressure that closes that gap is social rather than regulatory.
“People talk to each other a lot. References and word of mouth is extremely important,” Fakhouri said. He described the mechanism through a scenario regional banking executives will recognise. A CISO who learns that a competitor is quantum safe and certified starts asking internally when their own institution will be, and the question travels upwards from there. The same dynamic runs through government entities, healthcare, and financial services.
One finding underlines how regionally specific the transition has become. QuantumGate’s survey found that 98% of respondents consider sovereignty and home-built solutions important to post-quantum migration. The company builds and operates from the UAE, so the finding sits close to its commercial position and should be read with that in mind.
What it does suggest is that the migration is being treated regionally as a question of who controls the cryptography, not only of which algorithms replace which.
Fakhouri’s own summary of the priority order was unambiguous. “Inventory, plan, and ecosystem, top three most important aspects for PQC migration.”
For security leaders across the region who have secured budget and drafted a roadmap, the uncomfortable implication is that neither means very much until the first item is complete. A plan built on an incomplete picture of the cryptographic estate is a plan to migrate the systems you happen to remember.